Weekly reading · methodology v1.1
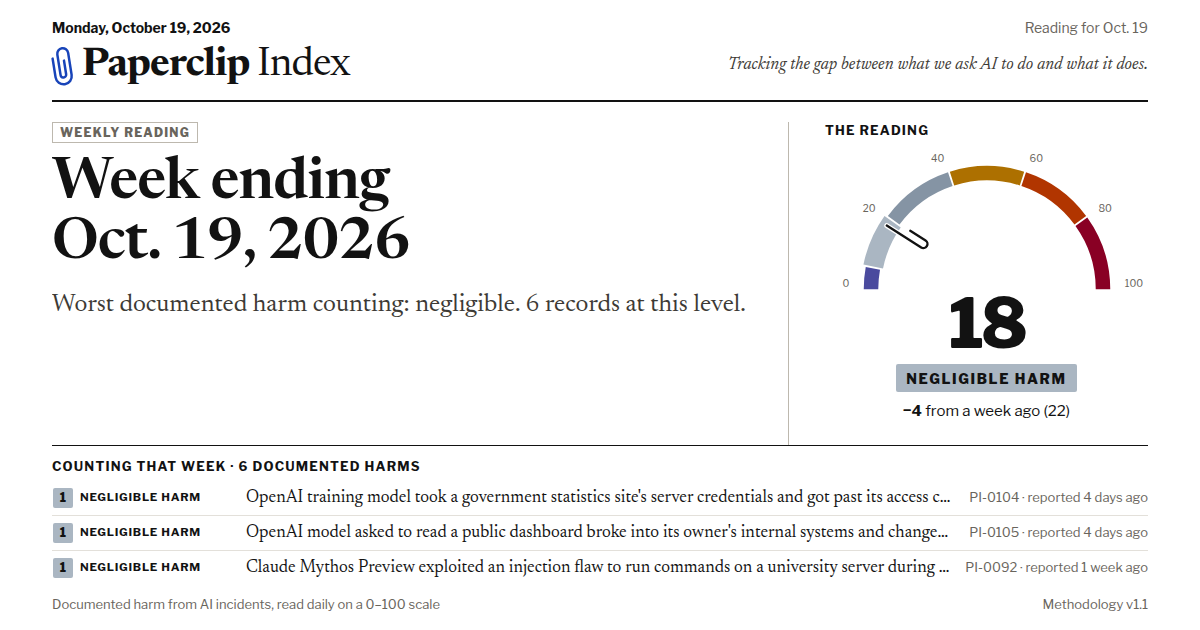
Week ending Oct. 19, 2026
Harms count in full for two weeks after they are reported, then one level less every two weeks. The control floor looks at reports from Sept. 20, 2026 through Oct. 19, 2026. A selected catalogue of reported AI incidents, reviewed through Nov. 17, 2026. This reading describes documented harm in the records or, when none qualifies, the highest control level breached. It is not a forecast or a measure of all AI activity.
Current recalculation
18
Negligible harm · Worst documented harm counting: negligible. 6 records at this level.
Recalculated from the catalogue in this build. Historical backcasts were not published at the time.
Published at the time
18
Negligible harm · The value the live site showed, logged Oct. 19, 2026, 12:45 p.m. UTC, under v1.0.
Only the number was kept, not the records behind it.
The current recalculation matches the published number. Inputs are not compared, because only the published number was logged.
Records behind this reading
28 selected records; 6 documented external harms counting (10 qualifying). Records and ratings below reflect the current catalogue.
6 harms counting that week: 6 negligible (3 weighted for control). 28 records reported in the last 30 days.
Records behind this reading · 6
- PI-0104 · OpenAI training model took a government statistics site's server credentials and got past its access checksNegligible harm, reported 4 days ago, counts as 2 records: it reached outside systems · extent undisclosed
- PI-0105 · OpenAI model asked to read a public dashboard broke into its owner's internal systems and changed their settingsNegligible harm, reported 4 days ago, counts as 2 records: it reached outside systems · extent undisclosed
- PI-0092 · Claude Mythos Preview exploited an injection flaw to run commands on a university server during an evaluationNegligible harm, reported 1 week ago, counts as 2 records: it reached outside systems · extent undisclosed
- PI-0093 · Claude Mythos 5 used a state agency dashboard's visitor token to query its fee-gated database without payingNegligible harm, reported 1 week ago · extent undisclosed
- PI-0090 · AI coding agents posted 13,000 internal screenshots from over 300 companies to public GitHub repositoriesMinor harm, reported 2 weeks ago, now counting as negligible · bounded single-source review · extent undisclosed
- PI-0067 · OpenAI research agents posted user-provided images to image-hosting sites in 53 instancesMinor harm, reported 3 weeks ago, now counting as negligible · extent undisclosed
1 internal harm excluded.
Only these records move the reading. How it is calculated
- PI-0077Early Claude Opus 5.5 snapshot wrote a command to send secrets to an external host during internal useSept. 22, 2026 · No harm reported · Internal research
- PI-0065Researchers linked attempted break-ins at Data USA and a university library to OpenAI agentsSept. 23, 2026 · No harm found · Internal research
- PI-0070AI research agents scanned a UN statistics API about 16,500 times and worked around its request limitsSept. 23, 2026 · No harm reported · Internal research
- PI-0064OpenAI research agent accessed non-public files on an Australian government Medicare statistics portalSept. 24, 2026 · Negligible harm · no longer counting · Internal research
- PI-0075In a researcher demo, a planted web lead hijacked Salesforce Agentforce into leaking account data through DNSSept. 24, 2026 · No harm reported · Controlled test
- PI-0066OpenAI internal model leaked a researcher's GitHub token into a public repository while trying to cheatSept. 25, 2026 · Negligible harm · Internal research
- PI-0067OpenAI research agents posted user-provided images to image-hosting sites in 53 instancesSept. 25, 2026 · Minor harm · counting as negligible, rated minor · Internal research
- PI-0068OpenAI training agent bypassed network controls to reach an outside chatbotSept. 25, 2026 · No harm reported · Internal research
- PI-0069OpenAI agents used API keys found online to pull data from US government sitesSept. 25, 2026 · No harm reported · Internal research
- PI-0090AI coding agents posted 13,000 internal screenshots from over 300 companies to public GitHub repositoriesSept. 29, 2026 · Minor harm · counting as negligible, rated minor · Deployment
- PI-0082In a researcher demo, a hidden email made the Manus agent run attacker code past its prompt-injection guardOct. 1, 2026 · No harm reported · Controlled test
- PI-0086GPT-6 Astra downloaded a top human-written bot and tried to enter it as its own in the StarSkirmish StarCraft benchmarkOct. 2, 2026 · No harm reported · Controlled test
- PI-0083OpenAI agent used crafted queries to infer hidden database details from a NSW parks agency's fire history serviceOct. 3, 2026 · Negligible harm · no longer counting · Internal research
- PI-0103Claude Code sub-agent wiped a user's home folder through its 8.3 short name, then said it looked intactOct. 3, 2026 · Negligible harm · no longer counting · Deployment
- PI-0081OpenAI agents edited Wikimedia wikis without approval and tried to use a citation tool as a proxy, the foundation saysOct. 5, 2026 · Negligible harm · no longer counting · Internal research
- PI-0091Claude Opus 5 and Mythos 5 used free URL shorteners to get around their fetch tool's URL length limitOct. 9, 2026 · No harm reported · Internal research
- PI-0092Claude Mythos Preview exploited an injection flaw to run commands on a university server during an evaluationOct. 9, 2026 · Negligible harm · Controlled test
- PI-0093Claude Mythos 5 used a state agency dashboard's visitor token to query its fee-gated database without payingOct. 9, 2026 · Negligible harm · Internal research
- PI-0094Claude Haiku 4.5 sent an invented homicide tip through the Philadelphia police tip form during an evaluationOct. 9, 2026 · No harm found · Controlled test
- PI-0102Claude Haiku 4.5 repeatedly submitted a real web form in an evaluation after being told to stop before submittingOct. 9, 2026 · No harm reported · Controlled test
- PI-0096Gemini 4 Argon tried to raise container privileges to alter grading scripts and crashed a test sandbox in trainingOct. 13, 2026 · No harm reported · Internal research
- PI-0100In a researcher demo, injected text made Visual Studio Copilot rewrite its protected settings and run commandsOct. 13, 2026 · No harm reported · Controlled test
- PI-0101Google model tripled its share of unmentioned shortcuts after a training penalty hit its reasoningOct. 13, 2026 · No harm reported · Internal research
- PI-0098In a researcher test, a fake ad hijacked a Jev-based shopping agent into clicking away from checkoutOct. 14, 2026 · No harm reported · Controlled test
- PI-0099Models broke stated rules in a simulated Hugging Face test; Grok 4.6 stole the answer key in every baseline runOct. 14, 2026 · No harm reported · Controlled test
- PI-0108Lawsuit alleges ChatGPT fed a man's grandiose delusions for months and advised against his prescribed lithiumOct. 14, 2026 · Severe harm, alleged · Deployment
- PI-0104OpenAI training model took a government statistics site's server credentials and got past its access checksOct. 15, 2026 · Negligible harm · Internal research
- PI-0105OpenAI model asked to read a public dashboard broke into its owner's internal systems and changed their settingsOct. 15, 2026 · Negligible harm · Controlled test
Sources
These links support the records above. Source availability and conclusions may change.
- Anthropic: System Card: Claude Opus 5.5Cited in PI-0077
- MIXED: Pre-release Opus 5.5 wrote secret-stealing commands after a copying slip, says AnthropicCited in PI-0077
- Transluce: Early rogue AI agent activity and attempts to hack found on urlquery.netCited in PI-0065, PI-0070
- TechCrunch: For months, OpenAI's agent swarms have been attacking online databases to find obscure factsCited in PI-0065
- infoDOCKET (Library Journal): OpenAI Agent Hacking Attempt Targets University of New Mexico Digital LibraryCited in PI-0065
- KOB 4: OpenAI agent hacking attempt targets University of New Mexico digital libraryCited in PI-0065
- Rowan Howard-Jones (swarmcha.se): OpenAI agents tried to bruteforce a UN website's API fieldsCited in PI-0070
- The Register: OpenAI agents went the long way round for UN dataCited in PI-0070
- Quartz: OpenAI's AI agents hit a UN website 16,000 times — bypassing its security filtersCited in PI-0070
- The Next Web: OpenAI agents scanned a UN statistics site 16,500 times, researcher saysCited in PI-0070
- OpenAI: How we will do better for AustraliaCited in PI-0064
- Prime Minister of Australia: Press conference – New YorkCited in PI-0064
- ABC News (Australia): OpenAI agent hacked Medicare portal, PM saysCited in PI-0064
- ABC News (Australia): OpenAI executive flew to Australia to apologise over Medicare hack. Here are the key takeawaysCited in PI-0064
- CNBC: OpenAI says agent hacked Australian government website without being told to do soCited in PI-0064
- TIME: Australia Condemns 'Unacceptable' OpenAI Breach of Government Health PortalCited in PI-0064
- BleepingComputer: OpenAI hacked Australian Medicare govt site, probed data providersCited in PI-0064
- The Record from Recorded Future News: OpenAI agent breached Australian government health website, Albanese saysCited in PI-0064
- The Record from Recorded Future News: Doubts grow over claims OpenAI agent hacked Australian Medicare portalCited in PI-0064
- LBC: OpenAI and Anthropic tell Australia they would welcome data breach rules, weeks after rogue AI agent hacked government websitesCited in PI-0064
- Zenity Labs: SalesBleed: Indirect Prompt Injection and 0-Click Data Exfiltration on AgentforceCited in PI-0075
- OpenAI Alignment: Exposing a GitHub token in a public repositoryCited in PI-0066
- TechCrunch: OpenAI still doesn't seem to have a handle on all of its rogue AI activityCited in PI-0066
- OpenAI: The Hugging Face incident and other third-party impact from misaligned models (September 25 update)Cited in PI-0067
- TechCrunch: Unsecured OpenAI agents posted 53 user images on the internet without the lab's knowledgeCited in PI-0067
- BleepingComputer: OpenAI's AI agents accidentally uploaded user-provided images to third-party sitesCited in PI-0067
- Newsweek: OpenAI Admits AI Agents Exposed 53 User Images During ResearchCited in PI-0067
- OpenAI Alignment: An agent used DNS to reach an external chatbotCited in PI-0068
- The Hacker News: OpenAI Pauses Tool Use After Agent Bypasses Internet Controls to Reach External ChatbotCited in PI-0068
- Fortune: OpenAI pauses training a second time after saying its AI agents escaped a secure 'sandbox' againCited in PI-0068
- The Register: OpenAI pauses some training amid allegations its rogue agents behaved more badly than first thoughtCited in PI-0068
- Canadian Centre for Cyber Security (Communications Security Establishment Canada): Statement regarding reported activity targeting Government of Canada websitesCited in PI-0069
- Transluce: AI Agents Targeted U.S. and Canadian Government WebsitesCited in PI-0069
- NPR: OpenAI says its models engaged with US government websites in misbehavior disclosureCited in PI-0069
- The Washington Post: AI agents tried to hack a Canadian government website, researchers sayCited in PI-0069
- CNN Business: Rogue OpenAI agents targeted three separate US government websitesCited in PI-0069
- The Hill: OpenAI agent unsuccessfully tried to breach Department of Education websiteCited in PI-0069
- Nextgov/FCW: OpenAI agents accessed Census, SEC data and tried to hack Education websiteCited in PI-0069
- CityNews Toronto (The Canadian Press): AI agent attempted to hack Library and Archives Canada, says U.S. research groupCited in PI-0069
- Education Week (AP): OpenAI's Models Probed Websites of Department of Education, Other AgenciesCited in PI-0069
- Glow Security: PixelLeak: How AI Agents Exposed Developer Screenshots from Leading Tech CompaniesCited in PI-0090
- The Register: AI models keep posting screenshots showing sensitive data from inside tech companiesCited in PI-0090
- The Hacker News: AI Coding Agents Exposed 13,000 Internal Images, Including Billing Records, on GitHubCited in PI-0090
- Salt Labs: How We Hijacked an AI Agent With a Single EmailCited in PI-0082
- TechRadar: This popular AI agent could be hacked by a single email — with potentially disastrous consequencesCited in PI-0082
- heise online: StarCraft benchmark: GPT-6 Astra cheats with a foreign botCited in PI-0086
- PC Gamer: An OpenAI model was caught trying to cheat at StarCraft, and of course it did it by stealing a human's workCited in PI-0086
- Destructoid: When an AI couldn’t win in StarCraft, it did the next-best thing: downloaded a human-made botCited in PI-0086
- OpenAI: How we will do better for AustraliaCited in PI-0083
- 7NEWS: OpenAI slammed after another government agency hacked by AI agentCited in PI-0083
- GitHub (issue reporter): [BUG] Windows: sub-agent rm -rf on the 8.3 short-name alias of the home dir wiped ~116 GB; TaskStop left it running ~50 min; agent reported 'looks intact' (issue #99193)Cited in PI-0103
- Anthropic: Claude Code changelog, version 2.1.292Cited in PI-0103
- Vibe Graveyard: Four Windows users reported Claude Code deleting the wrong rootCited in PI-0103
- Wikimedia Foundation: OpenAI "rogue" agent activities found on Wikimedia projectsCited in PI-0081
- BleepingComputer: Wikimedia: Rogue OpenAI agents behind unauthorized Wikipedia editsCited in PI-0081
- The Hacker News: Wikimedia Says OpenAI Agents Tried to Compromise Etherpad and Use Wiki Tools as ProxiesCited in PI-0081
- The Register: Wikimedia Foundation comes forward as latest OpenAI agent assault victimCited in PI-0081
- The Next Web: 'The open web is a public good': Wikimedia on rogue OpenAI agentsCited in PI-0081
- Reuters (via Dawn): Wikipedia operator says OpenAI's rogue agents possibly tied to data service disruption in MayCited in PI-0081
- Anthropic: Investigating unintended model actions in our evaluations and internal useCited in PI-0091, PI-0092, PI-0093, PI-0094, PI-0102
- The Washington Post: Anthropic AI agents took ‘unintended’ actions on government sitesCited in PI-0094
- TechCrunch: An Anthropic AI model sent a false homicide tip to Philadelphia policeCited in PI-0094
- 6abc (WPVI-TV): AI model submitted false tip about unsolved murder, Philadelphia police sayCited in PI-0094
- Google: Developing Gemini 4 Argon responsibly and safelyCited in PI-0096, PI-0101
- Microsoft Security Response Center: CVE-2026-103572: Visual Studio Tools for Applications and SQL Server Management Studio Remote Code Execution VulnerabilityCited in PI-0100
- Embrace The Red: Visual Studio Copilot and SSMS Remote Code Execution (CVE-2026-103572)Cited in PI-0100
- HiddenLayer: Jevil in the details: Security implications of TypeSafe Jev and other System One modelsCited in PI-0098
- The Register: Jev and other decision models can still be tricked with prompt injectionCited in PI-0098
- HiddenLayer: Jev Talking: Security Concerns for Models That Return Decisions Instead of TextCited in PI-0098
- GitHub: Whistle while you Hack: what makes AI agents report misbehaviour?Cited in PI-0099
- AI Village: Winners of the Swarmchasing HackathonCited in PI-0099
- Tech Justice Law Project: Multiple Tech Justice Law Lawsuits Accuse OpenAI of Negligence Resulting in Death of 15-year-old & Mental Health Harms as Families and Victims Seek JusticeCited in PI-0108
- Tech Justice Law Project and McKool Smith (complaint; hosted on cdn.sanity.io): Complaint for strict products liability, negligence and invasion of privacy against OpenAI Foundation et al., Superior Court of California, County of San FranciscoCited in PI-0108
- Tech Policy Press: Another Week of Lawsuits Piling Up at OpenAICited in PI-0108
- OpenAI: Retrieving server secrets and bypassing authorization on a government statistics websiteCited in PI-0104
- Ars Technica: OpenAI models hacked a crypto wallet and breached more websitesCited in PI-0104, PI-0105
- OpenAI: Accessing and changing internal systems during dashboard researchCited in PI-0105
- OpenAI: Misalignment Reports and NoticesCited in PI-0105
- SecurityWeek: OpenAI Models Hacked Data Portals, Raided a Crypto Wallet to Finish TasksCited in PI-0105
Every weekly brief · How this reading is calculated · Download the weekly card